Since 2 August 2026, most of the European regulation on artificial intelligence applies. With that deadline behind us, one question becomes very concrete for any company that has deployed AI: can you prove it?
Because that is where the AI Act is decided. The regulation does not ask for good intentions, nor for undertakings from suppliers. It asks for traces, documentation, logs, demonstrable human oversight. In other words: material evidence, produced by the system itself.
Two strategies answer that demand. The first stacks a compliance layer on a foreign cloud tool: procedures, registers kept by hand, screenshots, contractual promises. It is expensive, it is fragile, and it leaves a dependency on a supplier that Brussels is itself watching. The second chooses an architecture in which those obligations are not an added layer, but properties of the system.
That is the bet BrainDup made. Here is what it means technically, article by article.
Article 10, data governance: provenance is a constraint, not a metadata field
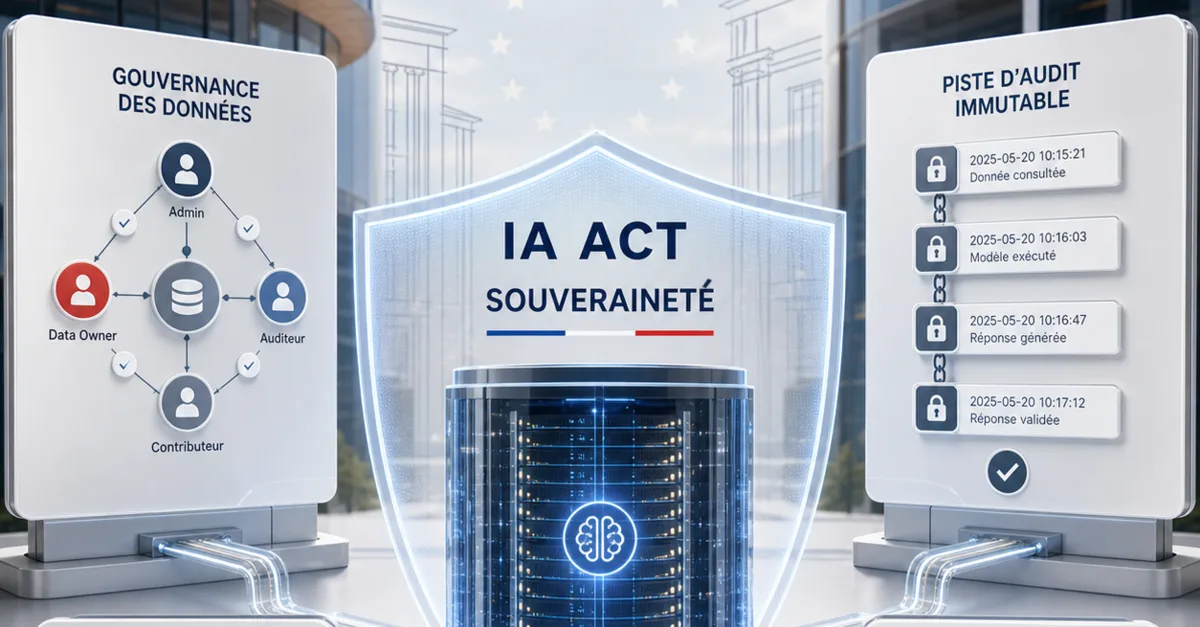
The regulation requires datasets to be relevant and representative, and their origin to be documented and governed. In BrainDup, provenance is not a field you fill in afterwards:
- a document's cryptographic fingerprint is computed before any processing, before text recognition, before extraction;
- every derived object (each text fragment, each vector, each node of the knowledge graph) carries the identifier of its provenance, its document, its source and its ingestion batch;
- a document already present cannot be silently re-ingested: the duplicate is caught by fingerprint and refused;
- distribution rights travel with the data itself, closed by default: what has not been explicitly opened stays internal.
The practical consequence: the question “where does this information come from?” does not call for an investigation. It calls for a query.
Article 12, event logging: logs the software itself cannot rewrite
The regulation requires automatic logging that allows the system's operation to be retraced. BrainDup keeps seven append-only audit logs, protected at the database level by triggers that physically forbid modifying or deleting a written row. This is not a development convention you can work around: it is a constraint of the engine.
Logged, among other things: every question asked and its reasoning trace, every document deletion, every human arbitration decision, every access, every quality evaluation.
One detail that matters: when a deletion partly fails (an unreachable store, say), the audit trail is written anyway, with the exact count of what was actually destroyed in each database. A system that only writes its traces when everything goes well records nothing useful.
Article 13, transparency: the model writes the answer, never the reference
Every answer cites its sources, and those citations are not written by the language model. They are assembled by the code from the document catalogue: author, number, date, page, address. The model never gets its hands on a metadata field.
That separation is strict, and its consequence is direct: a false citation is impossible by construction, not because the model would be reliable, but because it does not write the references.
The corollary is rarer in the industry than you would think: when the corpus does not hold the answer, the system refuses to answer. It does not fill the gap. An assertion without a source is treated as a blocking defect, on the same footing as the engine's other architectural invariants.
Article 14, human oversight: humans arbitrate where the machine hesitates
The regulation requires that people can supervise the system, intervene, and where necessary stop it. BrainDup places humans at the points of doubt rather than everywhere:
- low-confidence entity merges are arbitrated by a curator, never applied automatically;
- disputed or uncertain facts go into an arbitration queue;
- causal links are never inferred from mere co-occurrence: they require an explicit statement or human validation;
- every human decision is audited and reversible.
That last point deserves emphasis. Human oversight that leaves no trace is not oversight: it is a forgotten opinion.
Article 15, accuracy and robustness: measured, and measured without indulgence
The regulation asks for an appropriate level of accuracy, and above all for its measurement. BrainDup relies on empirical evaluation: a fixed set of reference questions, replayed on every change to the system, compared against the previous version. Three explicit thresholds: 100 % correct citations, at least 80 % correct answers, zero invention.
The technically important point: that evaluation is deterministic. No language model judges another language model; you do not measure an AI with an AI whose reliability is the very subject of the measurement.
Article 50: disclosing that you are talking to an AI, with no maintained ambiguity
The obligation is simple and BrainDup does not try to sidestep it: the interface states what it is. There is no imitation human adviser, and no ambiguity kept alive.
Articles 53 onwards, general-purpose models: the real tipping point
This is where the gap between the two strategies becomes structural.
Providers of general-purpose models carry obligations of their own, supervised by the European Commission. If your system rests on them, part of your compliance depends on a third party you do not control, whose terms of use, versions and availability change without you.
BrainDup runs entirely on your own infrastructure. The models are open and executed locally. No data leaves the company, and that is not a sales promise: it is a property verified automatically on every code change, by a blocking check that refuses any undeclared outbound dependency.
That changes the nature of the problem. You no longer hand your documents to a third party and hope it stays compliant. There is no handover.
Article 26, deployer obligations: what remains to be done, but with tools
The regulation requires the deployer to use the system in line with its instructions, to provide competent oversight, to retain the logs and to monitor operation. BrainDup supplies the material: access control through roles and permissions, a full log of the corpus lifecycle, a governance view, usage and cost statistics. What has to be done still has to be done, but with tools rather than a spreadsheet.
What BrainDup does not do for you
An honest article should say where the tool stops. No software makes an organisation compliant, and being wary of anyone promising it is a good habit.
Compliance is assessed per system and per use, not per product. Depending on what you do with it, your deployment may count as high risk, in which case you will run your own risk assessment, produce your technical documentation, appoint those accountable and, where applicable, complete the required formalities. BrainDup gives you the technical evidence; it does not write your file and does not take on your liability.
Likewise, training your staff remains yours to do. The regulation has required it since February 2025, and no tool discharges that duty for you; that is precisely what our training is for.
A final word on penalties, often quoted loosely. The ceiling of 35 million euros or 7 % of worldwide turnover applies to prohibited practices. Failing the obligations for high-risk systems falls in another band, around 15 million euros or 3 %. That remains substantial, and the reasoning does not change: an architecture that produces its own evidence beats a file reconstructed after the fact.
The heart of the matter
Regulating without an industrial strategy amounts to organising your own dependency. On that point we join those who remind us that open source remains, for mid-sized companies, the most accessible lever of sovereignty.
But an observation is not enough. The AI Act will not reward statements of intent; it will ask to see the logs, the traces, the sources, the decisions.
That is why, for us, these properties are not features bolted on afterwards. They are architectural invariants: rules the code cannot break, verified automatically, and everything else is built on them.
We agreed with the observation. We built the tool.
BrainDup is a sovereign document AI platform: ingestion, knowledge graph and sourced answers, on your own infrastructure. To talk it through, book a slot or write to us.
Sources
- Official Journal of the European Union: Regulation (EU) 2024/1689 laying down harmonised rules on artificial intelligence
- EU Artificial Intelligence Act: consolidated text and timetable
- AS3P (7 August 2026): “IA d'entreprise souveraine : BrainDup reste chez vous”, in French
- AS3P: “BrainDup, sovereign and secure AI for companies”
- Blog du Modérateur (2 August 2026): “IA Act, ce qui change au 2 août 2026”, in French
- Journal du Net: “IA Act, la régulation comme stratégie de soumission”, in French